


This feature first appeared in May/June 2024 and was published online on October 17, 2024. The expert’s statements and research examples below are presented in that historical context.
Additive manufacturing depends on digital files, software and connected equipment. Data theft, part alteration and production disruption can therefore have physical and economic consequences. These risks also affect other digital manufacturing processes; their combination within the AM workflow calls for an assessment tailored to that environment.
A 2020 survey of the America Makes community offers a bounded view of AM security concerns: 69 participants came from industry, agencies and academia, and 53 completed all questions. This sample describes respondents’ experiences and expectations; it does not establish a worldwide rate of cyberattacks specific to AM.
The task is to turn those concerns into practical priorities: which data need protection, which physical effects must be prevented, and which controls belong at each stage?
Different scenarios where AM-specific cybersecurity concerns may arise
One of the most mentioned AM-specific cybersecurity concerns is the case of design files that can be stolen. Other AM-specific cybersecurity concerns include the fact that design files can be changed to create flaws in parts, the toolpath can be modified to deposit materials incorrectly, dangerous or illegal parts or objects can be printed, digital twin or digital thread can be hacked, thus compromising maintenance or quality control.
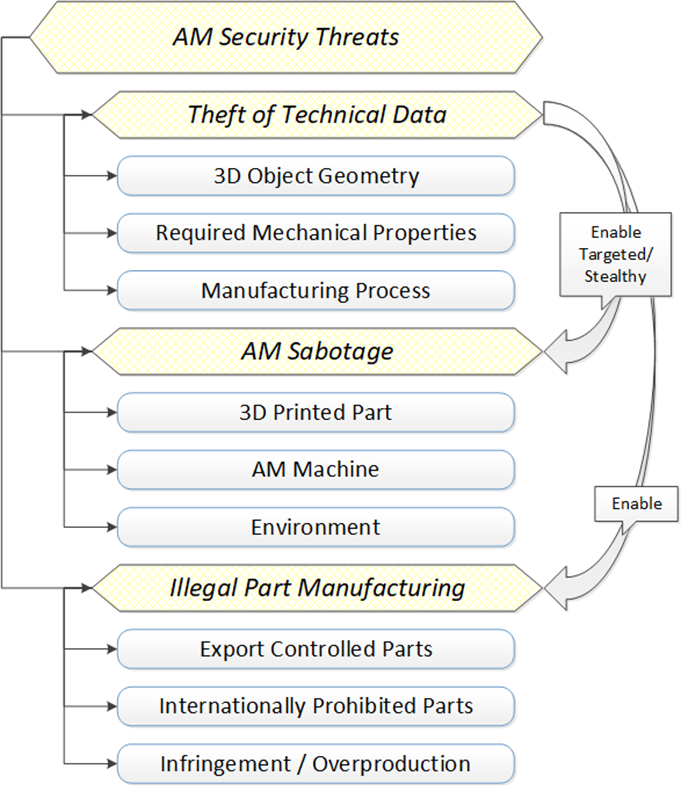
Mark Yampolskiy, then an Associate Professor of Computer Science and Software Engineering at Auburn University, summarizes these threats into three main categories.
“The first one is Technical Data Theft (TDT), which is commonly discussed in the context of Intellectual Property (IP) protection. However, not all data whose loss the defender would like to prevent is or can be protected as IP. Furthermore, there are kinds of data that a defender might consider negligible, but that can advance the attacker’s goals.
The second one is Sabotage, which is sometimes discussed in the context of integrity violation. However, not all integrity violations will lead to sabotage, and there are means to achieve sabotage without violating the classical integrity of cyber items, such as digital designs. In AM, sabotage can be directed immediately against the manufactured part or the machine. However, indirectly and more importantly, it can affect the system in which such part is integrated, or the environment of the AM machine.
The third is the use of AM for Illegal or Unauthorised Part Manufacturing (IPM). This is a threat distinct from the first two, because AM machines do not prevent manufacturing anything that is physically possible. Therefore, it is rather a legal concern for which a technical solution is sought.
Lastly, as AM Security is still a young discipline, it is likely that new threats will emerge. For example, we recently discovered that it is possible to embed additional information in the STL design file without affecting the design or printed part (using something known as ‘steganographic channels’). This threat does not aim at AM, but rather uses AM as an ‘accessory’ to further other attacks.
There are also ‘symbiotic relationships’ between threats. For example, TDT can be a precursor for a targeted sabotage attack (e.g., to design a defect for a specific part that will degrade its functional characteristics to a certain degree) or for IPM (e.g., to infringe parts using a stolen design). The steganographic channels in STL (and probably in other digital file formats used in AM) can be used to exfiltrate the stolen data ‘piggybacking’ on innocuous-looking design files sent outside a company or an organization.”
Potential impacts that may arise therefore include financial fraud, reputation damage or theft of IP, business disruption, destruction of critical infrastructure, threats to safety or even regulatory infringement.
So, how do you map these cybersecurity risks across the AM lifecycle?
As seen above, cybersecurity threats can occur at different levels. Therefore, it’s crucial to understand how data are transmitted and processed – and how information is communicated throughout the AM process, from design, build, and quality assurance monitoring, to testing, delivery, and distribution. Understanding that process comes down to establishing the digital thread specific to your organization and most importantly, identifying the stakeholder that could be impacted the most.
That stakeholder could be the AM equipment manufacturer, the 3D part designer, the material supplier, or the end customer.
Defining which stakeholder is impacted the most by a security threat in an AM workflow “depends on the threat we are talking about”, Yampolskiy outlines before adding: “original equipment manufacturers (OEM) and 3D part designers are probably the most affected by TDT. Their concerns might be different, though. The OEM is likely to be mostly concerned with their ‘secret sauce’, such as scanning strategy and process parameters for a specific material. The 3D part designers are likely to be more concerned about their design being stolen and infringed upon.
End customers are more affected if we talk about sabotage of parts. Having said that, an attack on the material supplier can be used to sabotage the feedstock to sabotage parts manufactured with it – a physical equivalent of what is known in cybersecurity as a ‘supply chain attack’.”
What steps can be taken to address AM cybersecurity threats?
First and foremost, it’s crucial to keep in mind that cybersecurity is not just an IT department issue. Therefore, everyone in the organization should be aware of the risks and ensure basic precautions are followed to prioritize safety.
If there is a scenario where we can’t address all the security challenges at the same time, defining the most important hurdle to address can be “a tough choice because different stakeholders might be more or less exposed to different threats. And this might change over time. Just two years ago I would answer the question by pointing at TDT. However, considering the current global instability and the return of great powers competition, I would say that Sabotage should be our main concern, at least for the time being”, the associate professor points out.
That being said, it’s never a bad idea to first conduct a thorough risk assessment to pinpoint the risks most pertinent to one’s specific AM scenario. This could also help pinpoint potential additional threats that might come into play with regard to AM applications.
One could also assess if lessons from well-known cyber-attacks could be applied to AM. According to a report from Deloitte on “3D opportunity and cyber risk management”, the “strategy, “test once, satisfy many,” can enable organizations to consider the applicable regulations in the same vein to avoid duplicating efforts, particularly when used in concert with design approaches that incorporate security directly into the design of products. They can then create a comprehensive risk management framework to evaluate their regulatory environment to best address their specific cybersecurity footprint. Given the fact that AM processes include both digital and physical components, a combination of strategies focused on both IT systems and physical objects may provide the most comprehensive initial approach.”
Protection begins in part with design files. At the time of this interview, Yampolskiy described work with Moti Yung (Google LLC and Columbia University), Nikhil Gupta (New York University) and Hammond Pearce (University of New South Wales) on a “solution for integrating robust digital watermark into STL design files.” This was a research direction, not evidence of an industry-wide deployment.
Protecting the printing process depends on the technology, IT environment, data and customer requirements. DISA’s Security Technical Implementation Guides (STIGs) address secure configuration; public versions are distributed through the DoD Cyber Exchange. Implementation, assessment and ongoing maintenance also require resources. At the time, Velo3D described a Sapphire system configuration assessed against selected STIGs. According to the manufacturer Velo3D, “in the realm of metal AM, the application of STIGs is particularly crucial due to the unique challenges and vulnerabilities inherent in this field.
The technology involves complex processes that integrate digital designs, advanced materials, and precision engineering. Each of these components introduces specific security risks that STIGs are designed to mitigate. For instance, the digital design files used in metal AM are highly sensitive. If compromised, they could lead to significant intellectual property theft and national security threats. STIGs provide comprehensive guidelines to secure these digital assets, ensuring that they are stored, transmitted, and accessed in a manner that minimizes the risk of unauthorized access or tampering.”
Compliance with STIG controls alone is neither authorization to connect to a DoD network nor a guarantee against every attack. The 2023 DISN Connection Process Guide requires assessment and an authorization decision for the relevant environment. Velo3D’s statements remain the manufacturer’s claims.
Other practices are seen in tracking and tracing. They include the use of RFID tags to track AM-produced products throughout the supply chain.
Speaking of a non-invasive solution that could be used to detect sabotage attacks, Yampolskiy explains they “use what is known as ‘side channels’, focusing on the power side channels of individual actuators. The approach has several advantages compared to pure cybersecurity solutions. To name just one, such an approach allows to air-gap the monitoring system from the monitored 3D printer, thus significantly increasing the difficulty of their simultaneous compromise. The project for the adoption of this approach to PBF is funded by NIST.”
Funding for research into detecting sabotage through actuator signals is documented in a 2021 Auburn announcement. The passage above describes work at the time of the interview, without establishing general production availability. A watermark or traceability tag alone does not replace a complete security approach.
Protection tailored to the risk
Improved protection can support trust in outsourced and on-demand manufacturing. It requires risk assessment, clear responsibilities and measures suited to the process. A 2022 NIST publication likewise emphasizes that technical controls, including encryption, must be complemented by a risk-based approach.
This feature was first published in the May/June 2024 edition of 3D ADEPT Mag.
Review note: the cyberattack percentages in the original introduction have been removed because their primary sources and scope could not be verified. The survey cited here has an identified sample. The interview quotations have been retained.
THE 3D ADEPT WEEKLY NEWSLETTER
The industry moves fast. Stay ahead.
Every week, the latest additive manufacturing news, in-depth features and real-world applications, straight to your inbox. Plus, be the first to know when a new issue of 3D ADEPT Mag is out.
Free · One email a week · Unsubscribe anytime
Clicking loads our email provider’s sign-up form, including its analytics and Google’s anti-bot protection. You’re only subscribed if you complete the sign-up. Read our privacy policy.